Manufacturers track machine uptime obsessively. When tracking OEE dashboards, production line efficiency, maintenance schedules, and so on, the cost of a line going down is visible, measurable, and taken seriously.
IT downtime gets treated differently. When the network goes down, the ERP freezes, or a server fails, the response is usually: call the IT guy, wait, get it fixed. The cost of the wait rarely gets calculated.
That's a problem, because the numbers are significant , and they're directly tied to one variable most manufacturers have never benchmarked: how fast their IT provider actually responds.
What downtime costs, by the numbers
According to Datto's 2025 SMB Technology Survey, the average small and mid-size business loses between $10,000 and $50,000 per major IT incident when you account for employee productivity loss, IT recovery labor, and revenue impact during downtime.
Let's look at the breakdown. If 20 employees are idled for 4 hours at an average loaded cost of $40/hour, that's $3,200 in direct productivity loss, before you factor in any IT recovery labor, any lost orders, any customer impact, or any production disruption.
Multiply that by three incidents a year (the industry average for SMBs) and you're looking at nearly $10,000 in labor cost alone, and potentially $30,000–$50,000 in total impact.
For a manufacturer with just-in-time production dependencies or time-sensitive customer commitments, the number climbs faster.
The response time variable
The single factor with the most leverage over your downtime cost is response time. Specifically, how quickly your IT provider engages and begins resolving the issue after you report it.
An IT provider who responds in 4 hours vs. one who responds in under 1 hour creates a roughly 3-hour difference in resolution start time. On a $40/hour loaded labor rate with 20 employees affected, that's $2,400 per incident or $7,200 per year at three incidents.
That's not a trivial number. And it's completely invisible until you calculate it.
The benchmark most manufacturers are missing
Most manufacturers don't have a formal response time SLA with their IT provider. They have a relationship. They have a phone number. They have a general sense that things usually get fixed "pretty quickly."
What they don't have is a documented guarantee or a contractual commitment that specifies: within X minutes, a qualified technician will be actively working on your issue.
Cyber insurance carriers are starting to ask about this. Not because response time is a coverage requirement yet, but because a slow-responding IT provider is a signal of overall IT maturity that underwriters are beginning to factor into risk assessments.
What to do with this information
Two things are worth doing now.
First, calculate your actual downtime cost. Use your real numbers, such as employees affected, average hourly cost, hours of downtime per incident, incidents per year. The calculator below takes 60 seconds and gives you a credible annual figure you can bring to a budget conversation.
Second, benchmark your current provider's response time against what you should expect.
If you want a direct conversation about where you stand, We ca do a free 20-minute Pre-Response Time Audit for manufacturers in the area — a structured review of your current IT response arrangement and what it's costing you.
For years, the standard ransomware advice was "make sure you have backups." But for ransomware in 2026, that advice is now incomplete in a way that's costing manufacturers weeks of downtime and, in some cases, the ransom payment they were trying to avoid.
The reason is: ransomware operators have updated their playbook. Before they encrypt anything, they find your backups. Then they encrypt or destroy those first.
According toVeeam's 2025 Data Protection Trends Report, over 93% of ransomware attacks now specifically target backup repositories as part of the attack sequence. The logic is straightforward: if the victim can restore quickly, they don't pay. So the attackers remove that option before they reveal themselves. While this trend isn't new, ransomware threats in 2026 follow the same playbook.
The IBM X-Force Threat Intelligence Index 2026documents this as a deliberate strategic shift, which the report calls "recovery denial." Attackers are systematically targeting backup infrastructure, identity services, and virtualization management layers specifically to eliminate the victim's ability to recover without paying.
What "recovery denial" looks like in practice
The attacker gains initial access typically through a phishing email, a compromised VPN credential, or an unpatched network appliance. Then they spend days or weeks moving laterally and mapping the environment. They're not looking for the crown jewels yet. They're looking for the backup server.
If your backup server is on the same network as your production environment and uses the same or similar credentials, they find it. They encrypt it first, or they delete the backup catalog, or they compromise the backup software console with admin access. By the time the ransomware payload executes across your production systems, your recovery option is already gone.
The three questions that determine your exposure
Whether your backups survive a ransomware attack comes down to three things. As ransomware by the end of 2026 is expected to become more sophisticated, these questions take on a critical new importance.
1. Are they reachable from the production environment?
Backups stored on a network-attached share accessible from the same domain, or a backup server that uses the same admin credentials as your production servers, sit inside the blast radius. An attacker who has compromised your production environment has a path to them.
The standard that carriers and auditors now require is immutable backups (data that cannot be modified or deleted for a defined retention period, enforced at the storage level) or air-gapped backups (physically or logically disconnected from the production network), and preferably both.
2. Do backup admin accounts share credentials with production accounts?
This is the most common gap. The backup software console is protected by a local admin account using the same password rotation schedule (or lack thereof) as everything else. An attacker with domain admin on your production environment has a short path to the backup console.
Backup infrastructure should be managed through dedicated accounts that exist nowhere else: separate credentials, separate MFA, separate access paths. If compromising your production admin account also means compromising your backup admin account, you have one layer where you need two.
3. Has a restore actually been tested?
This is distinct from the first two, but it matters for a different reason. Even backups that are properly isolated can fail to restore if the process has never been rehearsed. The most common scenario: backups have been running nightly for two years, nobody has performed an actual restore test, and when ransomware hits, the restore process fails or takes five times longer than expected because the team is running it for the first time under pressure.
Carriers now require documented restore tests, timestamped, with screenshots, completed within the last 90 days, not a backup job completion log.
How to find out where you stand
We built a short self-assessment (eight questions, two minutes) that scores your backup architecture against the criteria that ransomware operators are specifically targeting and that cyber insurance carriers are specifically requiring.
It doesn't ask for any system access or sensitive information. It asks about your architecture decisions. At the end, you get a score (Protected, At Risk, or Exposed) with a breakdown of which specific gaps your setup has.
If you'd rather talk through it directly, we can do a free 20-minute backup architecture review for manufacturers in the area. No pitch. Just a clear picture of where you stand before it matters as ransomware strategies in 2026 continue to shift.
Free 2-Minute Assessment
Is Your Backup in the Blast Radius?
Over 90% of ransomware operators target backup infrastructure first. Score your architecture against the exact criteria they exploit — and find out where you stand.
If you've sat through a CMMC assessment, a cyber insurance renewal, or a customer security questionnaire in the last year, you've noticed something: they all ask about the same things.
Not roughly the same things. The same five things, worded slightly differently depending on who's asking.
CMMC checks them. Your carrier checks them. And increasingly, your customers check them too, especially if they're a prime contractor, a regulated buyer, or anyone whose compliance team has woken up to the reality that their supply chain is their attack surface.
After looking at manufacturing breach data from IBM X-Force's 2026 Threat Intelligence Index, Palo Alto Networks' Unit 42 Incident Response Report, and the carrier underwriting requirements documented by Marsh McLennan and Coalition, the pattern is clear. Here are the five controls that matter, why they matter, and where most manufacturers are falling short.
1. MFA: Not Just Enabled. Enforced. And Increasingly, Phishing-Resistant.
Multi-factor authentication has been on every checklist for years. Now, carriers and auditors no longer accept "yes, we have MFA" as a passing answer. They want to know where it's enforced, whether it can be bypassed, and what type it is.
The distinction between "enabled" and "enforced" matters more than most IT teams realize. Enabled means MFA is available as an option. Enforced means nobody can authenticate without completing the MFA challenge. If an employee can choose to skip it, or if conditional access policies allow fallback to password-only from certain locations, you have a gap that both carriers and attackers will find.
The newer requirement, showing up on 2026 carrier applications and CMMC Level 2 assessments: phishing-resistant MFA. Standard push notifications and SMS codes can be intercepted by Adversary-in-the-Middle attacks in real time. FIDO2 security keys and passkeys use cryptographic authentication that can't be relayed because the verification happens between the physical device and the service directly.
For manufacturers with plant-floor workers who share workstations, rolling this out takes planning. It's not a weekend project.
The most common gap we see: MFA is enforced on Microsoft 365 but not on the VPN. The attacker doesn't need to get into email if they can get into the network.
2. EDR on Every Endpoint: Including the Ones Nobody Thinks About
Endpoint Detection and Response is the minimum standard now. Not antivirus. EDR. Every carrier application makes the distinction explicit, and most auditors will flag traditional antivirus as insufficient.
The difference: antivirus catches known threats by matching signatures. EDR monitors behavior patterns and can detect and isolate a compromised machine before the attacker moves laterally. In practice, this means EDR catches the 10pm lateral movement attempt that antivirus wouldn't notice until the ransomware payload executes three hours later.
The coverage requirement is where manufacturers get tripped up. "Every endpoint" means every device that touches your network. Not just the office laptops and desktops. Every server, every remote-access machine, and every device on the production floor that's connected to the business network.
For manufacturers running older operating systems on production-adjacent machines, some of those devices genuinely can't support a modern EDR agent. That's fine, but you need a documented exception with compensating controls. "We couldn't install it" is not a compensating control. "This device is segmented onto an isolated VLAN with no internet access and monitored by network-level detection" is.
The most common gap: EDR is on workstations but not on servers, and not on the HMI or engineering workstations that sit at the boundary between IT and OT.
3. Backups: Immutable, Tested, and Documented
This is the control that has evolved the most in the last two years. The bar has moved from "do you have backups" to "can you prove they work, and can an attacker destroy them."
The reason for the shift is simple math. According to multiple industry sources, over 90% of ransomware attackers now attempt to compromise or encrypt backups as part of the attack. If your backup infrastructure is accessible from the same network with the same credentials as your production environment, the attacker takes it out in the same sweep. Your recovery plan was sitting in the blast radius.
Carriers now want to see three things: that backups are immutable or air-gapped (meaning they can't be modified or deleted by anyone who has compromised your production environment), that they're stored off-network, and that you've completed a documented restore test within the last 90 days.
Not a backup job log showing the job completed. A restore test. Pull the data back, confirm it's intact, screenshot the process, timestamp it. That documentation is what separates a payable claim from a denied one.
The most common gap: nightly backup jobs run successfully and nobody has performed an actual restore test in over a year. The backup job completing is not evidence that the data is recoverable.
Free Download
The Manufacturer's Co-Managed Security Checklist
Five controls. Your team vs. your partner. One page.
4. Admin Rights: Reviewed, Minimized, and Documented
This is the control that feels the least urgent until you see how attackers actually operate. In nearly every manufacturing breach we've looked at, privilege escalation through over-provisioned admin accounts was part of the attack chain.
The pattern: an attacker gets initial access through a compromised credential or a phishing email. They land on a workstation with standard user rights. Then they discover that the IT admin account has a weak password, or that several employees have local admin rights that were granted three years ago for a software install and never removed, or that a former employee's account is still active with domain admin privileges.
From there, the attacker elevates to admin, accesses the domain controller, and has the keys to everything.
Carriers and auditors want to see that admin rights are actively managed: regular reviews (quarterly at minimum), immediate removal for departing employees, and a documented process for granting elevated access that doesn't involve "just give them admin so it works."
The most common gap: admin rights were granted for convenience at some point in the past and have never been formally reviewed. Nobody knows exactly who has admin access or why.
5. Patch Cadence: Including the Devices Nobody Patches
Servers and workstations generally get patched on a regular cycle. Patch management has been a standard IT practice for decades, and most organizations with any level of IT maturity handle this reasonably well.
The gap is in everything else. Firewalls, VPN concentrators, switches, access points, and OT-adjacent network devices. These are the systems that sit at the perimeter of your network, that are often directly accessible from the internet, and that attackers specifically target for initial access.
CVE-2021-22681 (the Rockwell Logix controller vulnerability that Iranian-affiliated actors targeted in early 2026) has been known since 2021. Five years. And thousands of devices remain unpatched and internet-facing. That's not an exotic zero-day attack. That's a known vulnerability on an unpatched device that was reachable from the public internet.
Carriers want to see a documented patch cadence that covers all device types, not just servers and workstations. If your firewall firmware is two versions behind, or your VPN concentrator hasn't been updated in 18 months, that's an active exposure that will show up on a carrier's external scan.
The most common gap: servers are patched monthly, but network appliances were last patched 12 to 24 months ago because "they're working fine and we don't want to break anything."
The Pattern That Matters
None of these five controls require exotic technology or massive budgets. What they require is consistent process, documentation, and someone who's tracking whether the work is actually getting done.
That last part is where the co-managed model fits for manufacturers with internal IT staff. Your IT person handles the day-to-day: distributing hardware tokens, coordinating maintenance windows, removing departed employees. A co-managed partner handles the parts that require specialized tools and continuous monitoring: configuring conditional access, running 24/7 EDR, managing immutable backup infrastructure, conducting quarterly audits, and producing the documentation that carriers and auditors want to see.
Neither side can do it alone. The internal person knows the business and the people. The partner knows the threat landscape and the compliance requirements. Together, the five controls get covered. Separately, at least two of them are always lagging.
We put together a one-page checklist that maps each of these five controls to what your internal team should own versus what a co-managed partner typically handles. It's specific to manufacturers and it's free.
Walk Through It Together
Score Results Review in 20 Minutes
Go control by control. Find out where you're solid and what to fix first.
There's a version of this article you've already read. It's the one where someone tells you MFA is important, backups matter, and you should talk to your broker before renewal. That version is useless to you. Here's the version that isn't.
In 2024, according to the National Association of Insurance Commissioners, nearly three times as many cyber insurance claims were closed without payment as those that were paid out. That's 28,555 claims denied versus 9,941 paid. For excess cyber policies, the ratio was worse: unpaid claims outnumbered paid ones by more than 20 to 1.
The insurance industry collected $16.3 billion in cyber premiums in 2025. That's nearly triple what it was five years ago. And they still lost money. Claims payouts reached $7.8 billion, ransomware incidents jumped 126% in Q1 2025 alone, and supply chain breaches now account for nearly 30% of all incidents.
Carriers responded the way you'd expect: they stopped trusting anyone.
Free Download
Cyber Insurance Renewal Readiness Checklist
See where you stand against what carriers are requiring in 2026. Takes about five minutes.
If you renewed a cyber policy before 2024, you probably remember the application as a formality: a few pages, some yes/no checkboxes, maybe even a conversation with your broker. The carrier took you at your word.
That's over. According to Marsh McLennan's 2025 Cyber Insurance Market Report, 99% of cyber insurance applications now include specific questions about MFA implementation. Not "do you have MFA," but "is MFA enforced across email, VPN, RDP, cloud applications, and all admin accounts, and can you provide documentation."
Some carriers are running technical scans of your external network before they'll even issue a quote. They're checking for exposed ports, unpatched systems, misconfigured DNS, and known vulnerabilities. This happens before you've signed anything.
The questionnaire is now an audit. And if your answers don't match what they find, you either don't get coverage, or you get coverage that won't pay when you need it.
What's worse, given the data reported by NAIC, unless you shore up and document everything to fit the requirements, even if you get renewed, your claim will be denied should you file one.
The Five Controls That Actually Matter
Every carrier's requirements are slightly different. But after looking at what's showing up consistently across major underwriters in 2026, there are five controls that appear on virtually every application.
1. Phishing-Resistant MFA, Not Just MFA
This is the biggest change from even a year ago. Standard MFA, the kind that sends a push notification to your phone or a code via SMS, is no longer considered sufficient by many carriers. The reason: Adversary-in-the-Middle attacks have gotten good enough to intercept and replay MFA tokens in real time. An employee clicks a convincing phishing link, enters their credentials, approves the push notification, and the attacker captures the session token before it expires. MFA was technically in place. It still failed.
Carriers are now asking specifically about phishing-resistant MFA, which means FIDO2 security keys or passkeys. These use cryptographic authentication that can't be intercepted because the authentication happens between the physical key and the service, not through a channel an attacker can sit in the middle of.
For manufacturing environments, this is a significant lift. You likely have employees who don't sit at desks, who share workstations, who access systems from the plant floor. Rolling out FIDO2 keys to that population takes planning. Start now if your renewal is in the next six months.
Coalition's 2024 Cyber Claims data found that 82% of denied claims involved organizations without fully implemented MFA. That single statistic should inform how you prioritize your next 30 days.
2. EDR on Every Endpoint, Not Just the Office Machines
Endpoint Detection and Response EDR) is the successor to traditional antivirus, and carriers now distinguish between the two explicitly. Antivirus looks for known bad files. EDR monitors behavior, detects anomalies, and can isolate a compromised machine before the attacker moves laterally through your network.
The key word carriers use is "every endpoint." Not just the laptops and desktops in the front office. Every server, every remote machine, every device that touches your network. For manufacturers, this includes machines in the shop that might be running older operating systems that don't support modern EDR agents, which creates a documentation challenge: you need to show the carrier either that EDR is installed or that you have a documented exception with compensating controls.
If a breach occurs and the carrier finds that the endpoint where the attacker gained initial access didn't have EDR, your claim is in trouble.
3. Immutable, Tested Backups
This one has evolved the most. Two years ago, carriers wanted to know if you had backups. Last year, they wanted to know if you tested them. This year, they want to know if your backups are immutable, meaning they can't be modified or deleted by an attacker who has gained access to your network.
The reason for the shift: 94% of ransomware attackers now attempt to destroy or encrypt backups as part of the attack first. If your backup infrastructure is connected to the same network and accessible with the same credentials as your production environment, the attacker takes it out along with everything else. Your "backup" was sitting in the blast radius the whole time.
Carriers want to see air-gapped or immutable backups stored off-network, with documented restore tests completed within the last 90 days. Yes, actual restore tests, with screenshots and timestamps, proving you pulled data back and it was intact.
For a manufacturer running 24/7 production, testing a full restore is operationally disruptive. Do it anyway. Do it on a weekend. Document it thoroughly. That documentation is what stands between you and a denied claim.
4. Written Incident Response Plan
Not "our IT guy knows what to do." A written plan. With named roles, contact information, escalation procedures, communication templates, and a decision tree for whether to pay a ransom or attempt recovery.
Carriers want to see that you've thought about this before it happens, because the data overwhelmingly shows that organizations without written IR plans take longer to contain breaches, lose more data, and incur higher costs. The plan doesn't need to be 50 pages. It needs to exist, it needs to be current, and your team needs to know where it is.
5. Vendor Risk Documentation
This is the newest addition to the standard underwriting checklist, and it catches a lot of manufacturers off guard. Carriers are now asking whether you've evaluated the security posture of third-party vendors who connect to your systems. Your ERP provider, your MES vendor, your managed print service, your third-party IT support, your payroll processor: anyone with network access or access to sensitive data.
The logic is straightforward. Third-party vendor incidents now account for roughly 20% of all cyber claims. An attacker who compromises your vendor gets a trusted connection into your network. If you can't show that you've assessed those vendors and documented their security controls, you're carrying a risk that carriers are increasingly unwilling to cover.
What "Denied" Actually Looks Like
The denial statistics are alarming, but they don't tell the full story of how denial happens. It's rarely a carrier saying "no" at renewal. More often, it plays out like this:
You have a policy. You've been paying premiums for years. An incident occurs. You file a claim. The carrier sends an investigator. The investigator finds that MFA was enabled on email but not on the VPN. Or that backups existed but hadn't been restore-tested in eight months. Or that EDR was on the office machines but not on the server where the attacker gained access.
The carrier points to the application where you attested that these controls were in place. They call it material misrepresentation. The claim is denied.
This isn't hypothetical. In the International Control Services v. Travelers case, coverage was denied after Travelers discovered that MFA was implemented on the firewall but not on the remote access system the attackers actually used. The business thought they had MFA. They did, technically. Just not where it mattered.
S&P Global Ratings has forecast a 15 to 20% premium increase in 2026 following two years of declining rates, driven by the ransomware surge and the credential theft explosion. The carriers who were competing on price two years ago are now competing on selectivity. They want fewer, better-prepared clients, and they're willing to let the rest go.
What This Means for Manufacturers Specifically
Manufacturing sits in a uniquely difficult position on cyber insurance. It is, according to IBM's X-Force Threat Intelligence Index, the most attacked industry in the world for the fifth consecutive year. Manufacturing production environments run legacy systems that can't always support modern security tools. Your OT networks often share infrastructure with your IT networks. Your downtime costs are immediate, measurable, and significant.
Carriers know all of this and they price it accordingly. Average cyber insurance premiums for mid-size manufacturers ($10M to $50M revenue) now run $3,500 to $10,000 per year, with larger operations paying $10,000 to $30,000 or more. And those are the premiums for manufacturers who can demonstrate the five controls above. For those who can't, the number goes up fast, or the application comes back declined.
The average ransomware payment in manufacturing exceeded $400,000 in 2026, with total event costs (including recovery, business interruption, and legal exposure) commonly reaching $1 million to $5 million for mid-size operations. Your carrier knows this number because they've paid it. They don't want to pay it again for a business that couldn't prove MFA was enforced.
There's also a CMMC angle here that's worth mentioning. If you're a manufacturer in the defense supply chain, CMMC 2.0 enforcement begins in November 2026. Many of the controls CMMC requires overlap directly with what carriers are asking for. Getting your cyber insurance documentation right is essentially doing double duty: it positions you for both renewal and compliance.
The 2026 Coverage Exclusion Problem
Here's the development that should genuinely concern every business owner reading this: carriers are now adding explicit coverage exclusion clauses for incidents that could have been prevented with basic controls.
This goes beyond denying claims after investigation. This is language written into the policy itself that says: if the incident was caused by a failure to maintain the controls you attested to, the policy does not apply.
The practical effect is that your premium buys you less than it used to. You're paying for a policy that only covers you if you were already doing everything right. If you weren't, you're self-insured whether you know it or not.
What to Do in the Next 30 Days
If your renewal is in the next six months, here's the sequence that matters:
Week 1: MFA Audit Document everywhere MFA is currently enforced. Every system, every access point. Identify gaps. If you're still on SMS or push-only MFA for privileged accounts, start the migration to phishing-resistant MFA now. Order FIDO2 keys this week if you don't have them.
Week 2: EDR Inventory Pull a report from your EDR vendor showing every device covered. Cross-reference it with your full device inventory. Identify any machines that don't have EDR and determine whether they can support it. For those that can't, write a documented exception with compensating controls.
Week 3: Backup Restore Test Schedule and execute a full restore test. Not a backup verification, a restore. Pull the data back, confirm it's intact, screenshot the result, timestamp it. Store the documentation somewhere your IT team and your broker can access it.
Week 4: Documentation Package Compile your incident response plan (write one if you don't have one), your vendor access list with security assessments, your MFA coverage map, your EDR deployment report, and your backup test results into a single folder. This is your evidence package. When the carrier asks, you hand them this.
The Uncomfortable Bottom Line
Cyber insurance in 2026 is not a safety net. It's a qualification process. The carrier is not your advocate, your partner, or your advisor. They are a business that has lost billions on claims from businesses that weren't prepared, and they have restructured their entire underwriting model to make sure they don't lose that money again.
The businesses that will maintain affordable coverage are the ones that can prove, with documentation, that they had the right controls in place before the incident occurred. Not after. Not during. Before.
Everything else is a policy that looks good in a drawer and fails when you need it.
If you're a manufacturer in Southeast Wisconsin and you'd rather have someone walk through this with you than figure it out from a blog post, we can do a free 20-minute cyber insurance readiness review. We'll tell you where you stand and what to fix first, and if everything checks out, we'll tell you that too.
Rather Talk It Through?
Book a Free 20-Minute Readiness Review
We will look at where you stand against what carriers are requiring and tell you what to fix first. No pitch, no obligation.
The cybersecurity threats Wisconsin manufacturers face are no longer limited to stolen files or suspicious emails. When ransomware hits a production environment, it can escalate fast: CNC machines stop receiving job files, shipping slows down, ERP data becomes unavailable, supervisors lose visibility into work orders, and the plant floor starts making decisions with incomplete information.
That is why manufacturing has become such an attractive target. Attackers know many manufacturers run lean IT teams, older production systems, remote vendor connections, and tight delivery schedules. A bank can freeze transactions. A manufacturer may have to stop a line.
National threat data now backs up what many Wisconsin IT directors already feel: manufacturing is under heavier pressure than most industries. IBM reported thatmanufacturing was the most attacked industry for the fourth consecutive year in 2024, with the highest number of ransomware cases among industries it tracked.
The Numbers: What the Threat Data Means for Wisconsin Manufacturers
The clearest takeaway from the 2023–2025 data is this: ransomware is now an operations problem, not just an IT problem.
Dragos documented 1,693 ransomware attacks against industrial organizations in 2024, an 87% increase over the prior year, and found that 75% of ransomware incidents it responded to caused a partial OT shutdown while 25% caused a full OT shutdown.
For a Wisconsin manufacturer, that can mean delayed shipments, overtime recovery, missed contract obligations, and customer confidence problems.
Verizon’s 2025 manufacturing breach data also shows why mid-sized manufacturers are exposed. In manufacturing breaches, ransomware appeared in 47% of cases, stolen credentials in 34%, exploited vulnerabilities in 23%, and phishing in 19%. Verizon also found that more than 90% of breached manufacturing organizations in its sample were SMBs with fewer than 1,000 employees.
That matters because many Wisconsin manufacturers operate exactly in that range: large enough to be valuable, but not large enough to run a 24/7 security operations center. Zscaler’s 2025 ransomware research found manufacturing was the most frequently hit sector in its data, with 1,063 attacks over the prior year, while U.S. victims accounted for 50% of ransomware attacks globally.
Locally, the 2023 ransomware attack involving Fincantieri Marinette Marine showed what that risk looks like on the shop floor. USNI News reported that the attack affected servers used to feed instructions to CNC manufacturing machines and knocked some systems offline for several days.
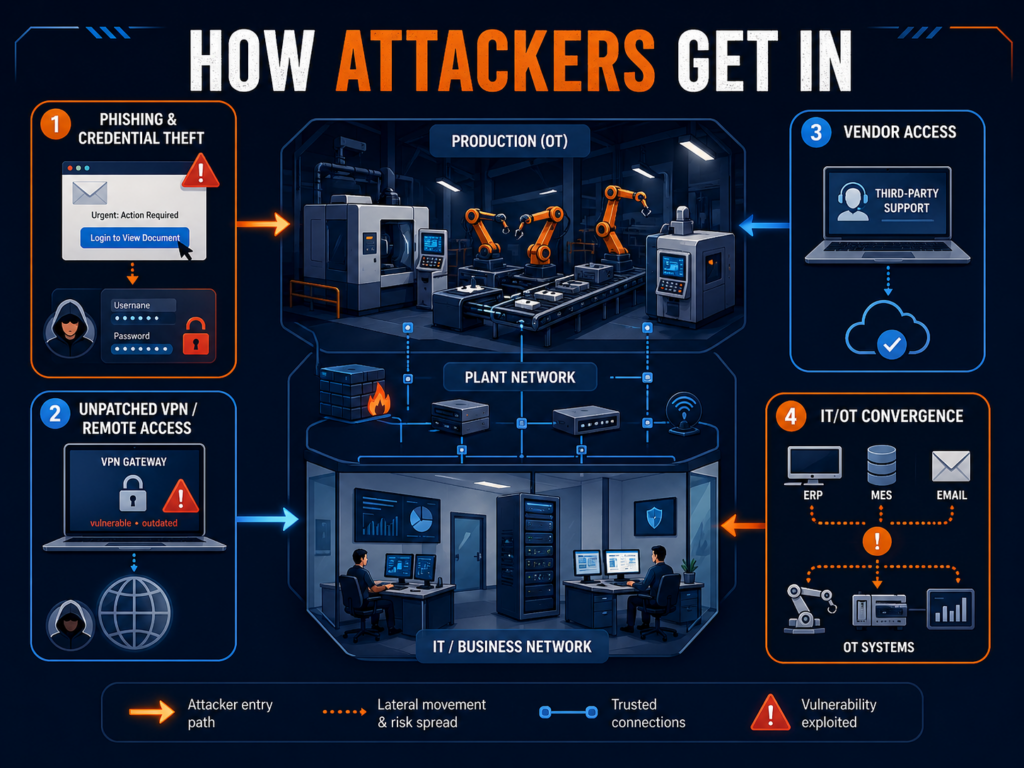
How Attackers Get In
Most manufacturing ransomware attacks do not start with movie-style hacking. They start with access that should have been harder to use, easier to monitor, or closed months ago.
1. Phishing and Credential Theft
A phishing email in a manufacturing business rarely looks like a generic scam. It may look like a supplier invoice, a freight update, a customer drawing, a quote request, or a Microsoft 365 login prompt sent to a plant manager rushing between meetings.
Once attackers capture a password, they try to log in like a real employee. IBM reported that stolen credentials surged 71% year over year and represented 30% of incidents it responded to in 2023, tied with phishing as the top infection vector.
In a plant environment, that one login can lead to email access, file shares, ERP systems, CAD files, or maintenance documentation. If multi-factor authentication is missing from VPN, admin accounts, or email, the attacker’s job gets much easier.
2. Unpatched VPN and Remote Access
Manufacturers rely on remote access for good reasons. Engineers connect after hours. Vendors support equipment. IT teams troubleshoot without driving to the plant. The problem is that VPNs, firewalls, and remote access portals are some of the first doors attackers check.
Verizon’s 2025 SMB snapshot noted that exploitation of vulnerabilities has become the most common initial access vector in ransomware breaches, driven heavily by attacks on perimeter devices.
For manufacturers, the risk is not just “someone got into the network.” The risk is that an old VPN account, unpatched firewall, or shared vendor login gives an attacker a path toward the systems production depends on.
3. Vendor Access
Manufacturing runs on outside access: machine vendors, ERP consultants, managed software providers, maintenance contractors, logistics platforms, and sometimes customers with portal access. Each relationship may be necessary. Each one also creates a door.
The issue is usually not that vendors are careless. It is that access is often granted once and reviewed rarely. A vendor account may stay active after a project ends. A shared login may exist because “that’s how the machine vendor set it up.” A remote support tool may be installed on a workstation nobody has inventoried.
When attackers find those paths, they do not need to break down the front door. They walk in through a service entrance.
4. IT/OT Convergence
The phrase OT IT security manufacturing sounds technical, but the business issue is simple: the office network and production network are now more connected than they used to be.
ERP talks to scheduling. Scheduling talks to production. Engineers push files to machines. Supervisors pull reports from plant-floor systems. Remote monitoring tools collect equipment data.
That connectivity helps manufacturers move faster, but it also gives attackers more ways to turn an IT incident into an operations event. The Fincantieri Marinette Marine incident is a practical example: the impact was not limited to email or back-office disruption; it touched networked operations tied to CNC workflows.
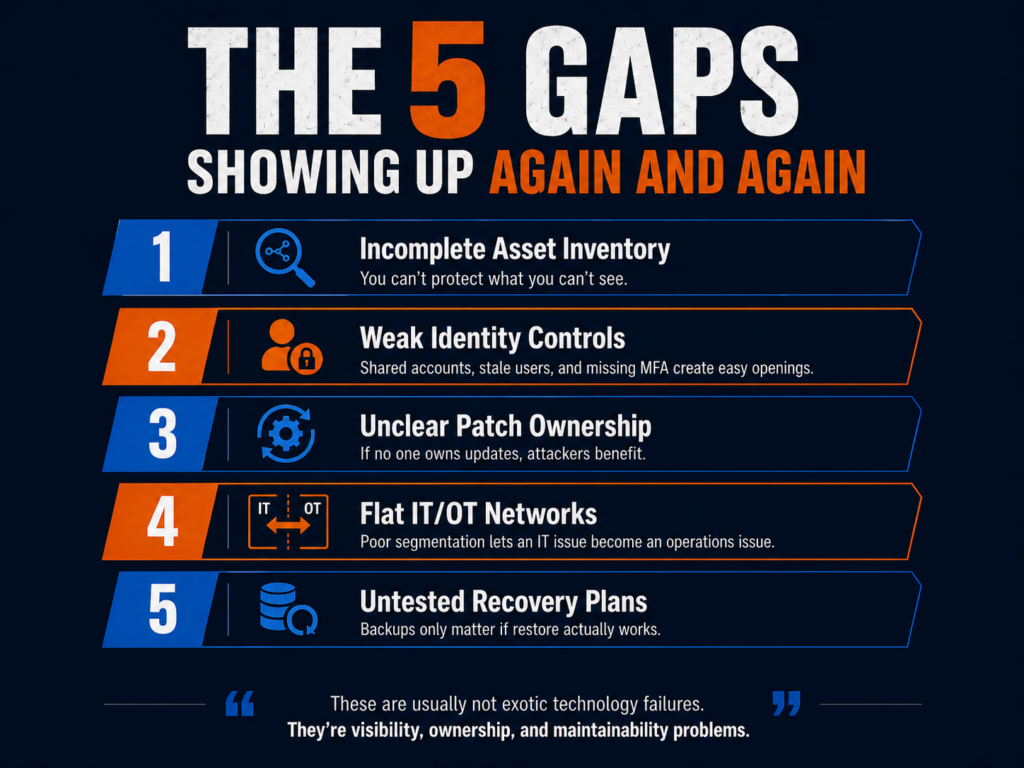
The 5 Gaps Showing Up Again and Again
The pattern in the data is not that manufacturers are being beaten by exotic attacks. The pattern is that attackers keep finding the same gaps: access, patching, documentation, segmentation, and recovery.
“The future of the Industrial Heartland depends on its ability to defend the digital code that now governs its physical machines.”
Here are the five gaps Wisconsin manufacturers should pay attention to first.
1. Incomplete asset inventory.
You cannot protect what you cannot see. Many manufacturers know their servers and laptops, but not every vendor tool, engineering workstation, old switch, remote access appliance, or production-connected PC.
2. Weak identity controls.
Shared accounts, stale users, missing MFA, and standing admin rights give attackers room to move. This is especially risky for executives, IT admins, engineers, and vendor accounts.
3. Unclear patch ownership.
IT may patch Windows systems, but who owns firmware, firewalls, VPNs, HMIs, PLC support stations, and vendor-managed equipment? When nobody owns the patching calendar, attackers benefit.
4. Flat networks between IT and OT.
If ransomware can spread from a compromised office workstation into production-adjacent systems, the business has a segmentation problem. Segmentation is not about making the plant harder to use. It is about making a bad day smaller.
5. Untested recovery plans.
Backups are helpful only if they restore quickly and completely. Cyber insurers and customers increasingly expect evidence: restore tests, logs, incident response plans, and documented roles. Current cyber insurance renewal guidance, for example, focuses on MFA, EDR, backup restore testing, and evidence gathering as practical readiness steps.
For defense suppliers, this also connects to compliance. The Department of Defense CMMC program rule became effective December 16, 2024, and phased CMMC implementation began November 10, 2025. For aCMMC Wisconsin manufacturer, cybersecurity documentation is no longer just a best practice. It can affect contract eligibility.
What IT Directors Are Doing About It
Many Wisconsin manufacturers do not need to replace their IT teams. They need to stop asking a small internal team to do every job at once.
That is where the co-managed IT model is gaining traction. Internal IT keeps ownership of the business: users, systems, plant priorities, ERP projects, production needs, and leadership communication. A co-managed cybersecurity partner adds the pieces that are hard to staff internally, such as continuous monitoring, patch compliance tracking, endpoint detection, log review, incident response planning, backup validation, and security documentation.
This model works well for manufacturers because it respects how plants operate. Production cannot wait for a generic enterprise security program. IT needs help that fits maintenance windows, vendor realities, older systems, and uptime requirements.
The best co-managed relationships also produce evidence. That matters for cyber insurance, customer audits, CMMC readiness, and executive reporting. Your co-managed IT partner can provide you with help and documentation around MFA, role-based access, incident response plans, backup testing, vendor controls, and any other cybersecurity policy controls are needed. Here you can find anUltimate Compliance Checklist we put together for Milwaukee businesses.
The Warning Is Clear, but So Is the Path Forward
The 2023–2025 threat data tells a clear story: manufacturers are high-value ransomware targets because downtime hurts immediately. For Wisconsin manufacturers, this is not a distant national trend. The local and sector-level evidence shows attackers are already focused on production-heavy environments, remote access, stolen credentials, vendors, and IT/OT weak spots.
The good news is that the biggest improvements are practical. Start with visibility. Lock down identity. Patch the systems attackers actually use to get in. Segment production from office IT where it matters. Test recovery before a crisis. Document the work so leadership, insurers, auditors, and customers can see progress.